Share on social
Sep 22, 2026
Lorem ipsum
What’s new
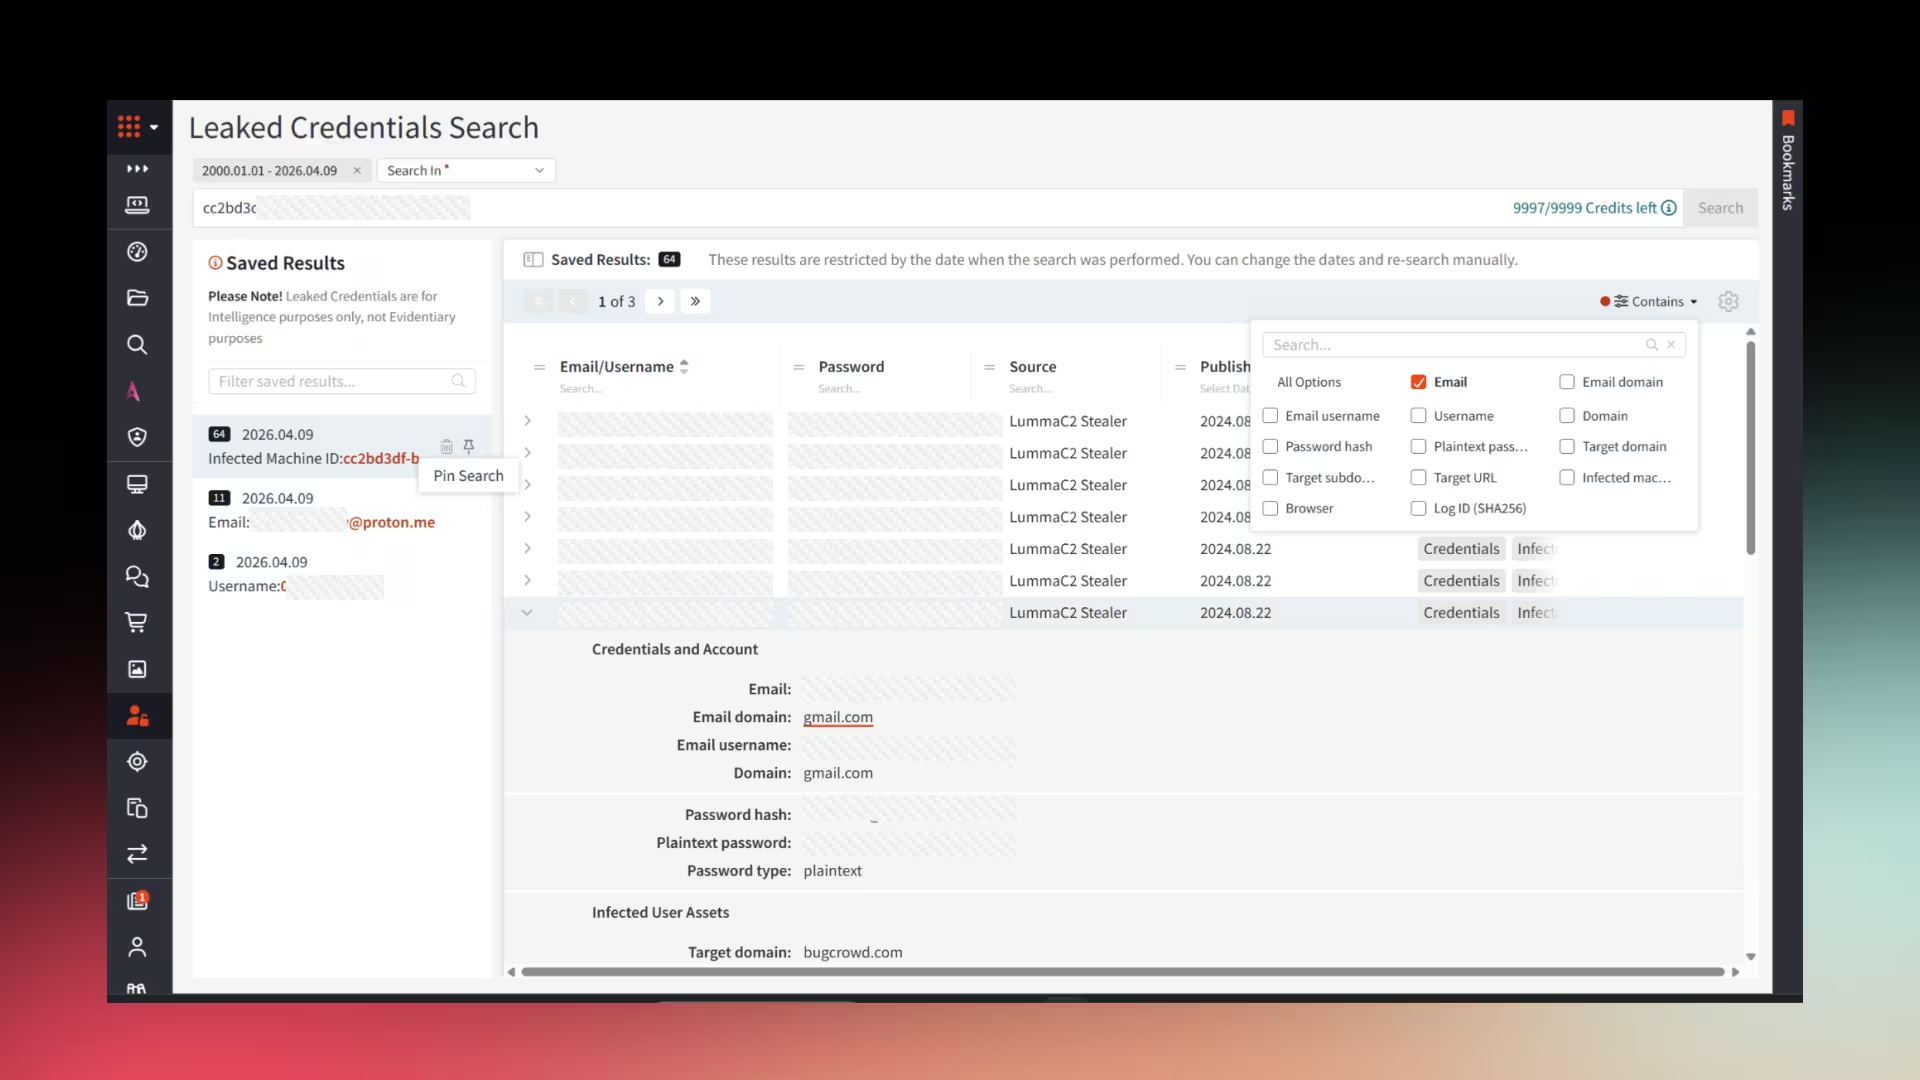
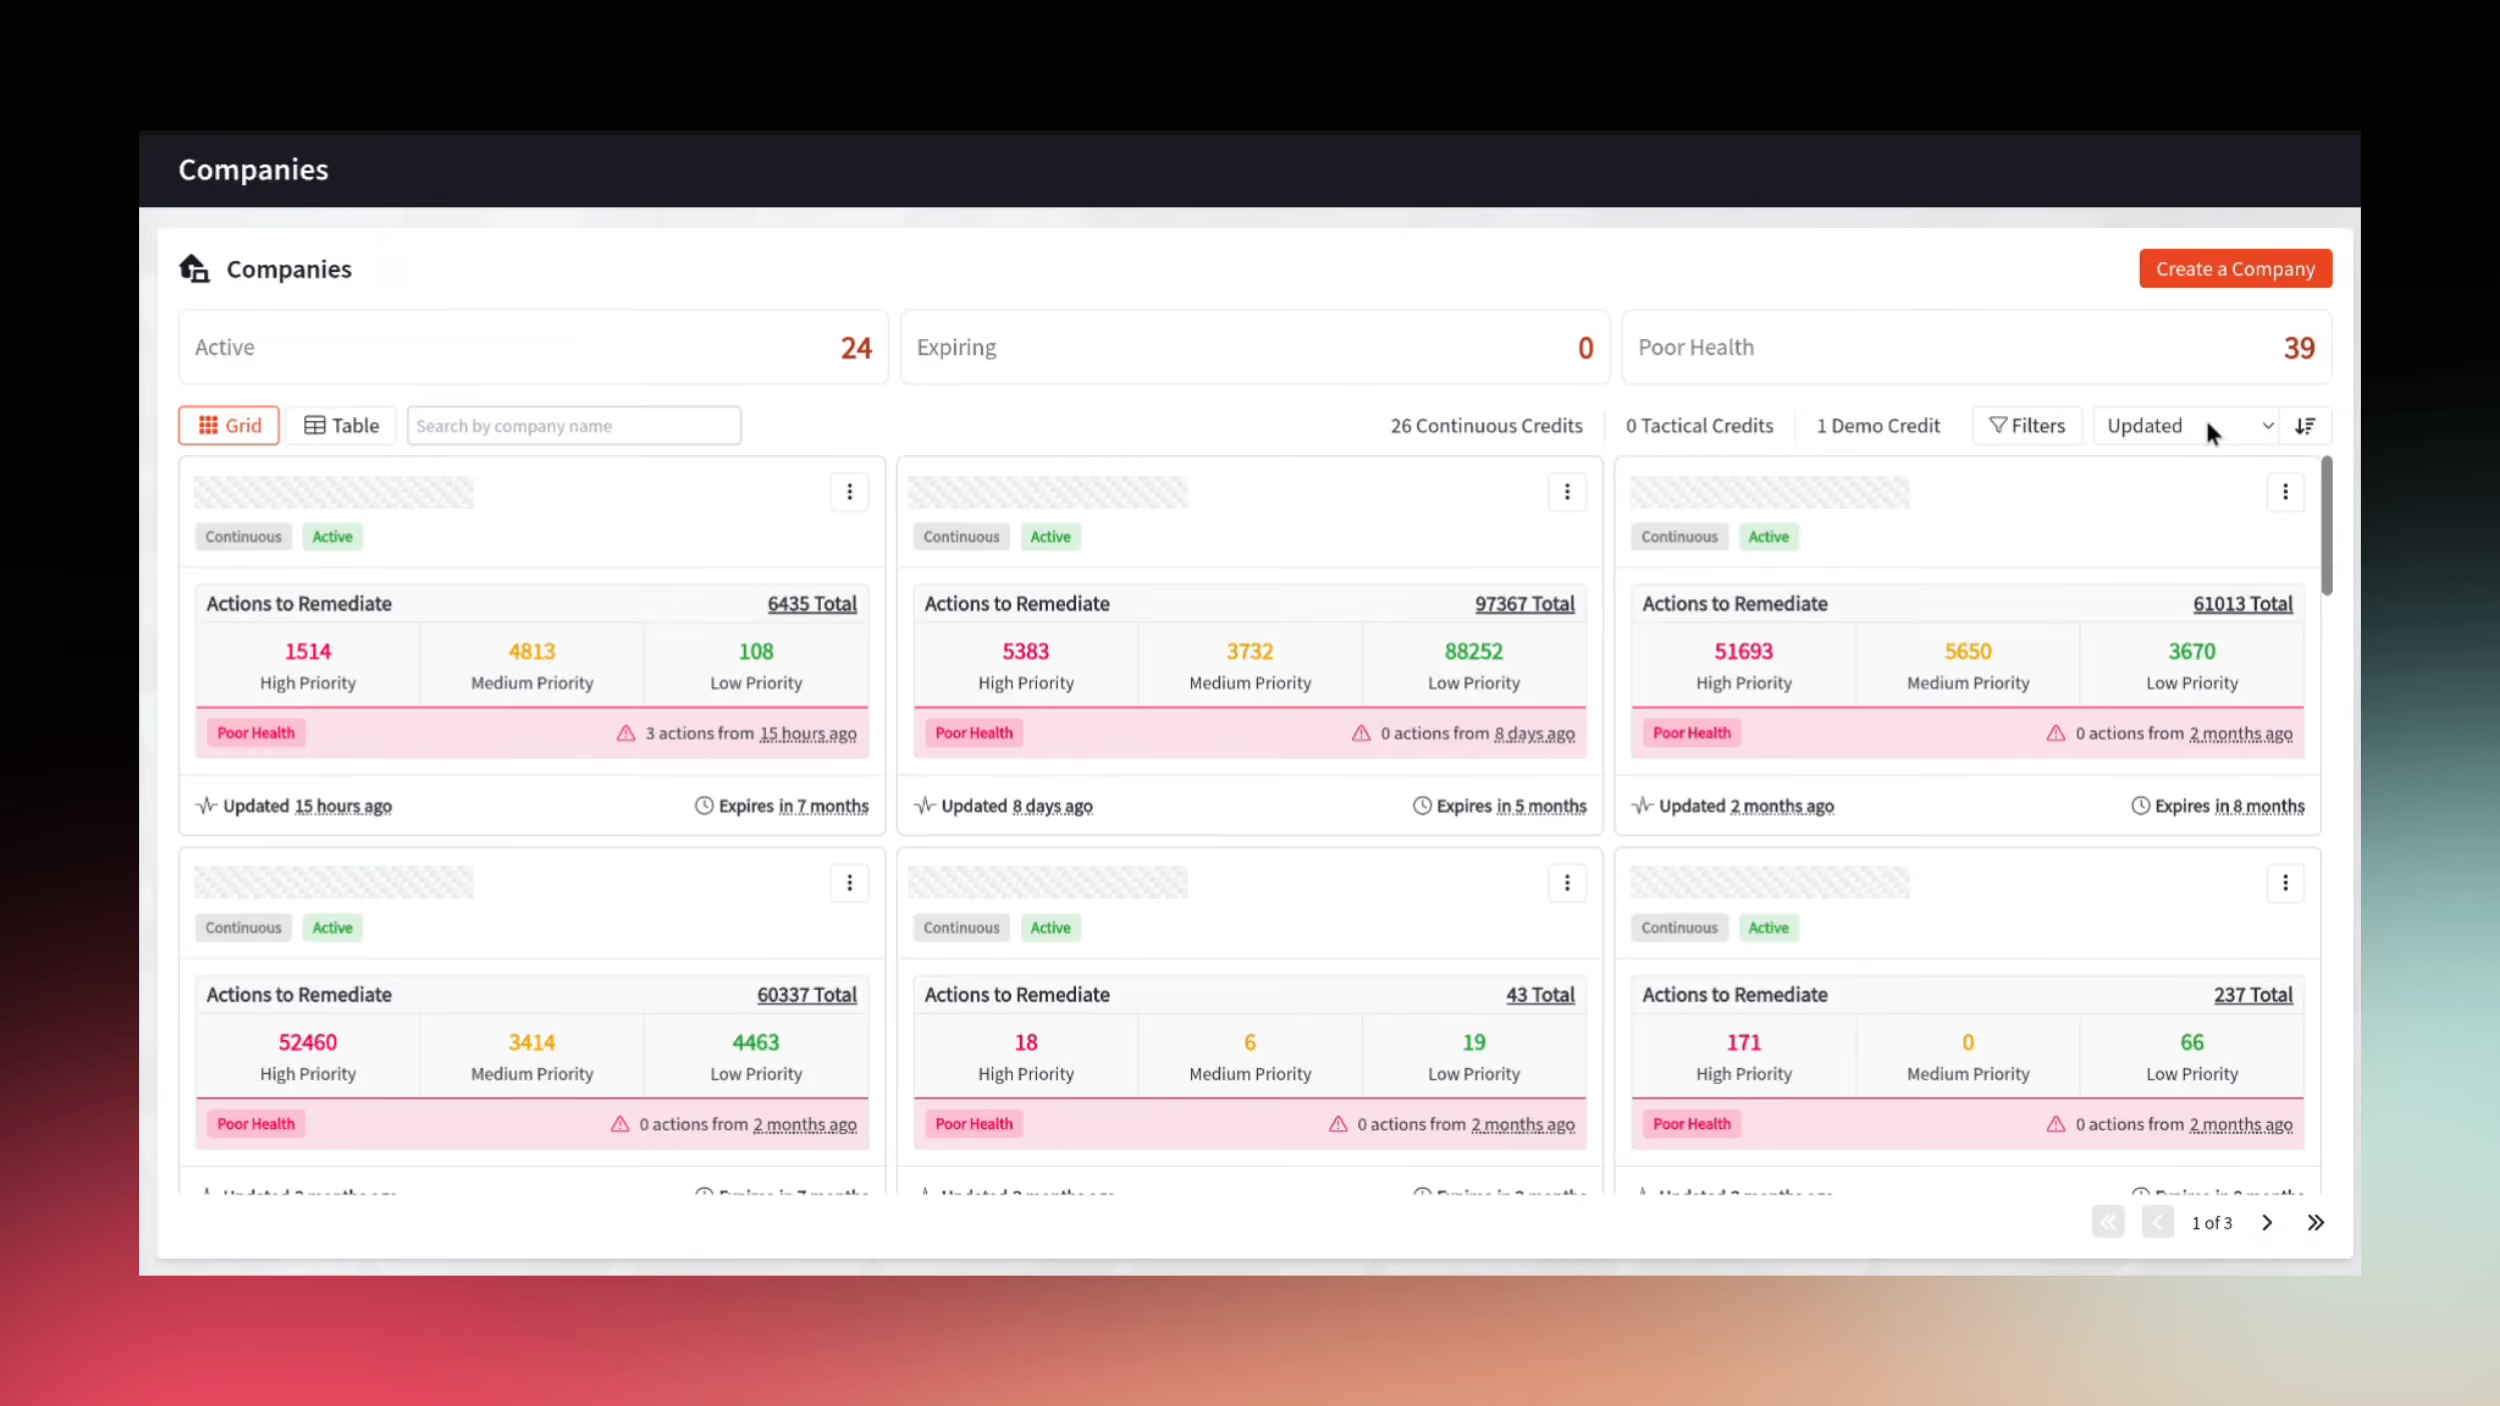
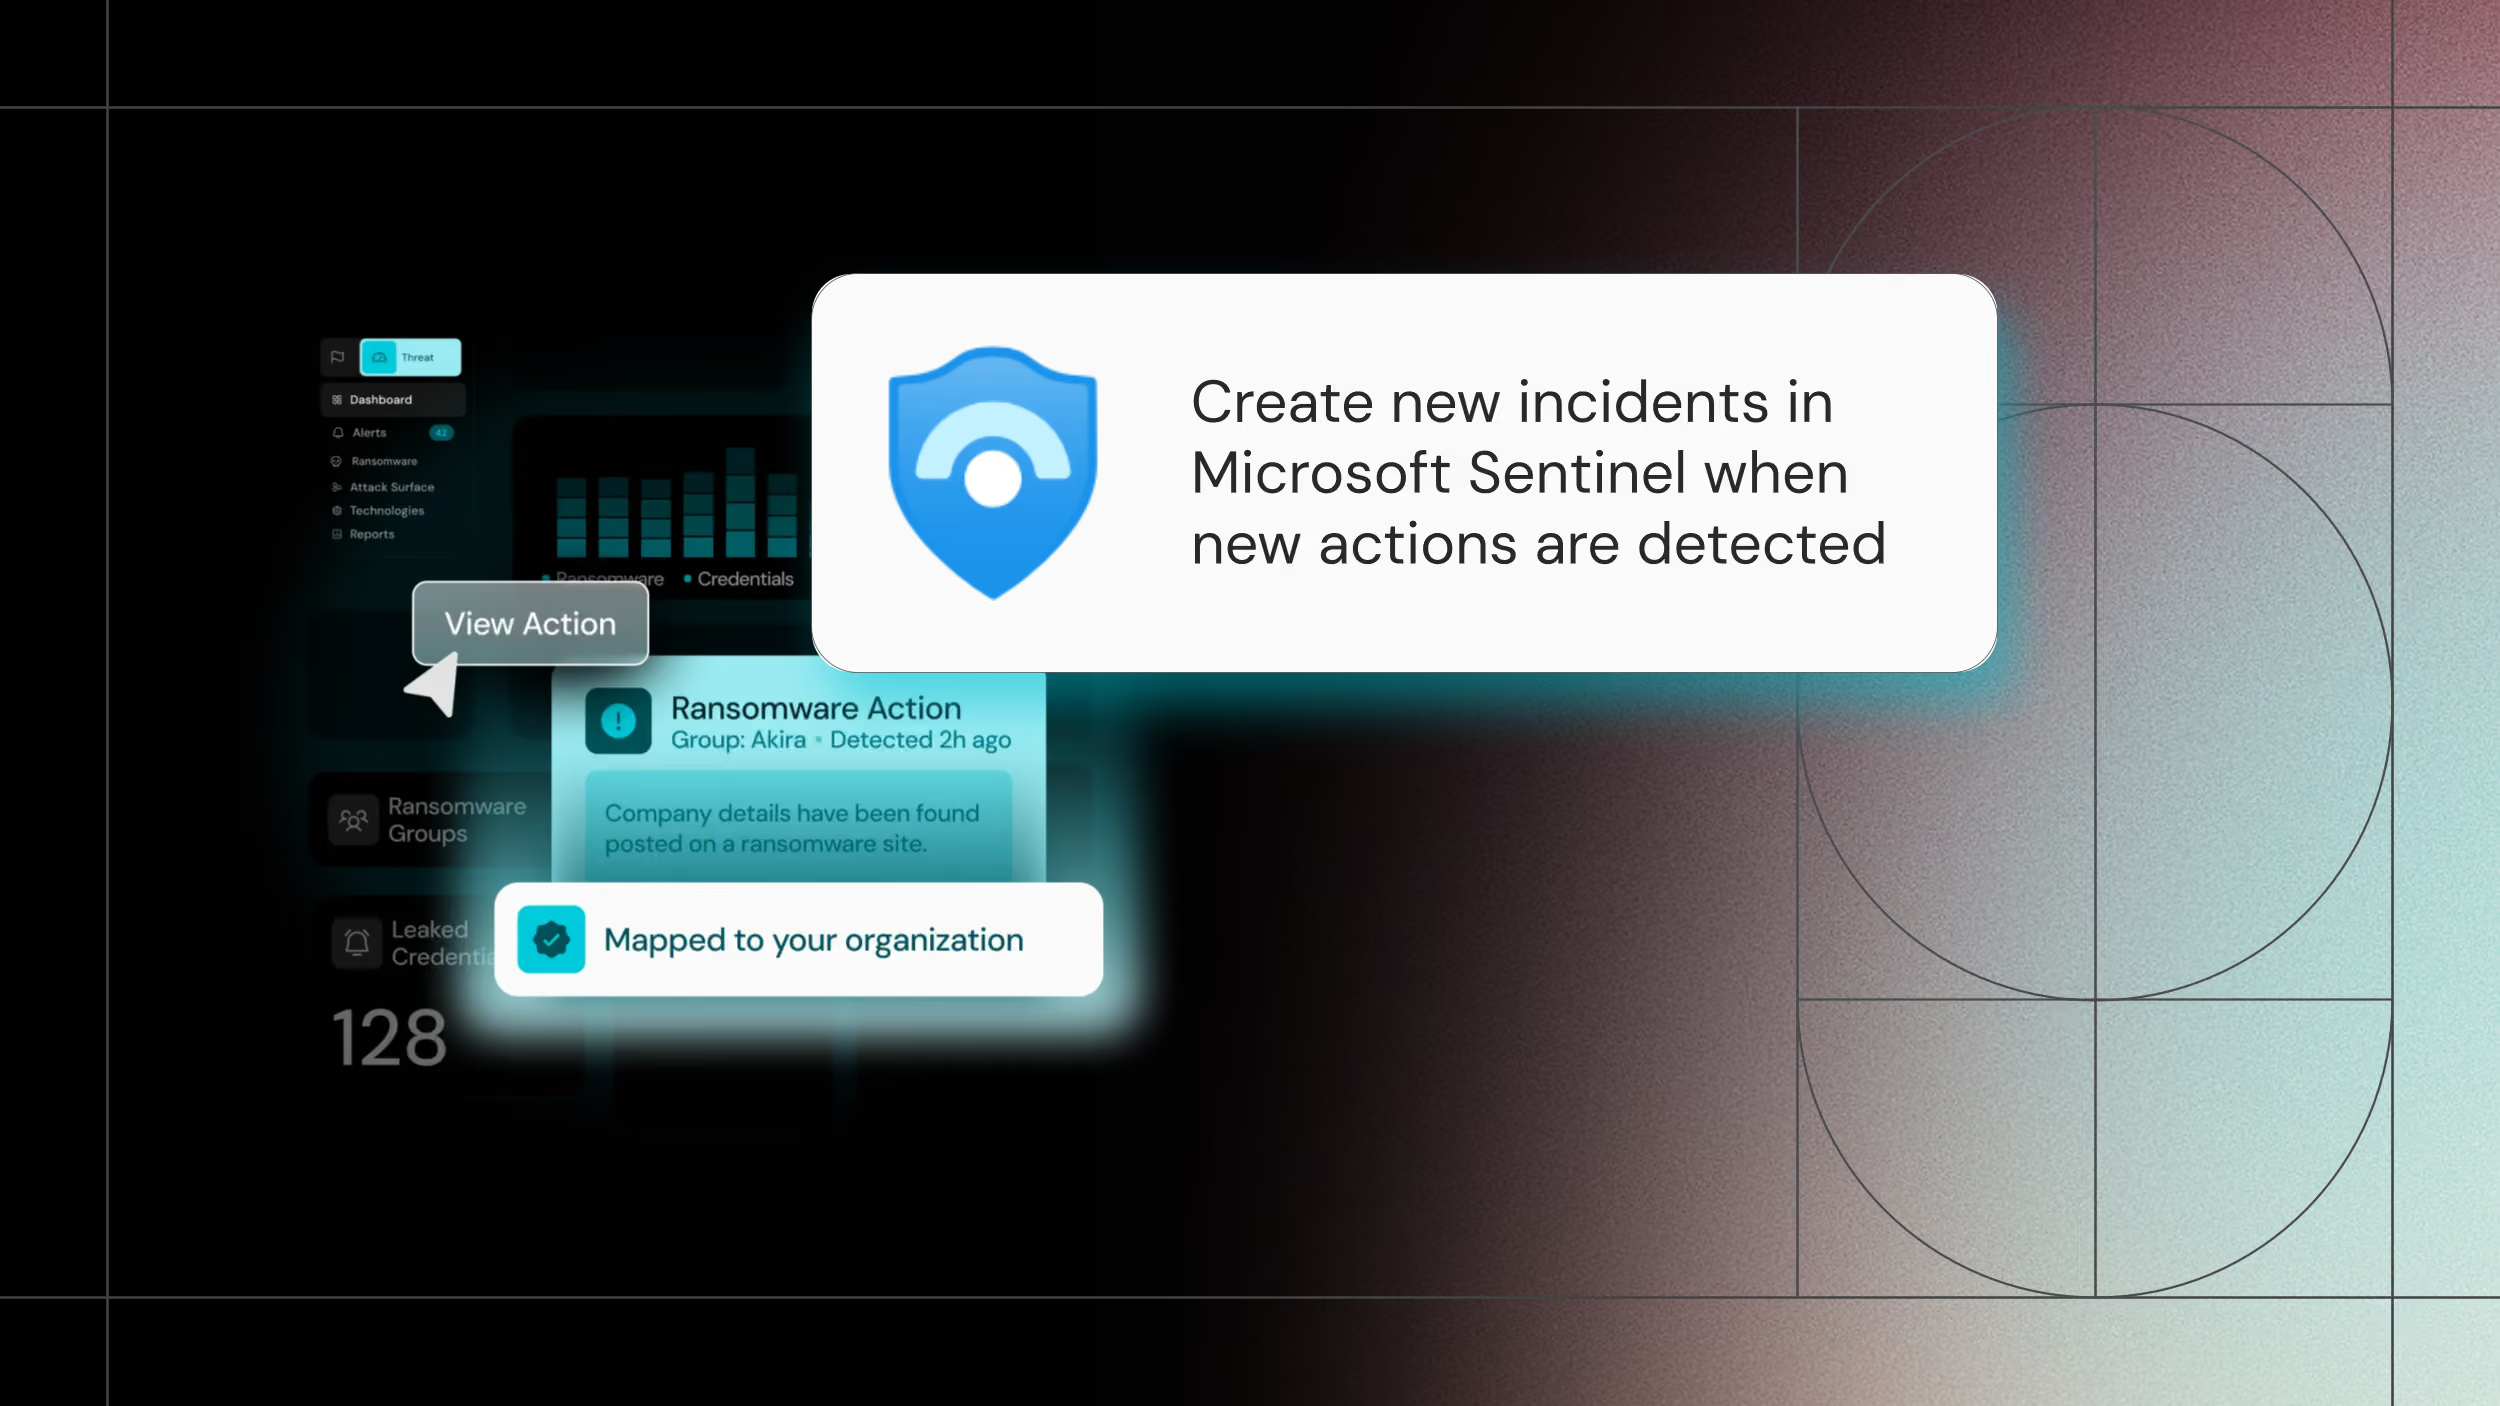
Security teams can now connect Searchlight Threat – Monitor with their instance of Microsoft Sentinel, to automatically create incidents – and triage them using rules you define whenever new pre-attack signals are detected.
Key benefits
Organizations with an existing Microsoft Sentinel instance can ingest and create rules for actions discovered in Searchight’s Monitor platform, adding our clear, deep, and dark web web intelligence to everything already flowing into their SIEM. Within Sentinel, teams can build automated rules to triage incoming actions, based on the type and severity scoring, so the highest-priority threats get routed for rapid response without the need for manual sorting.
This complements Searchlight Exposure's existing Sentinel integration, giving teams full visibility of both pre-attack Actions and attack surface vulnerabilities in one place
How it works
Full documentation on how to set up the new integration and sending a test notification to validate successful implementation of the integration can be found in the product documentation, available from the Integrations center.