Share on social
Sep 22, 2026
Lorem ipsum
What’s New
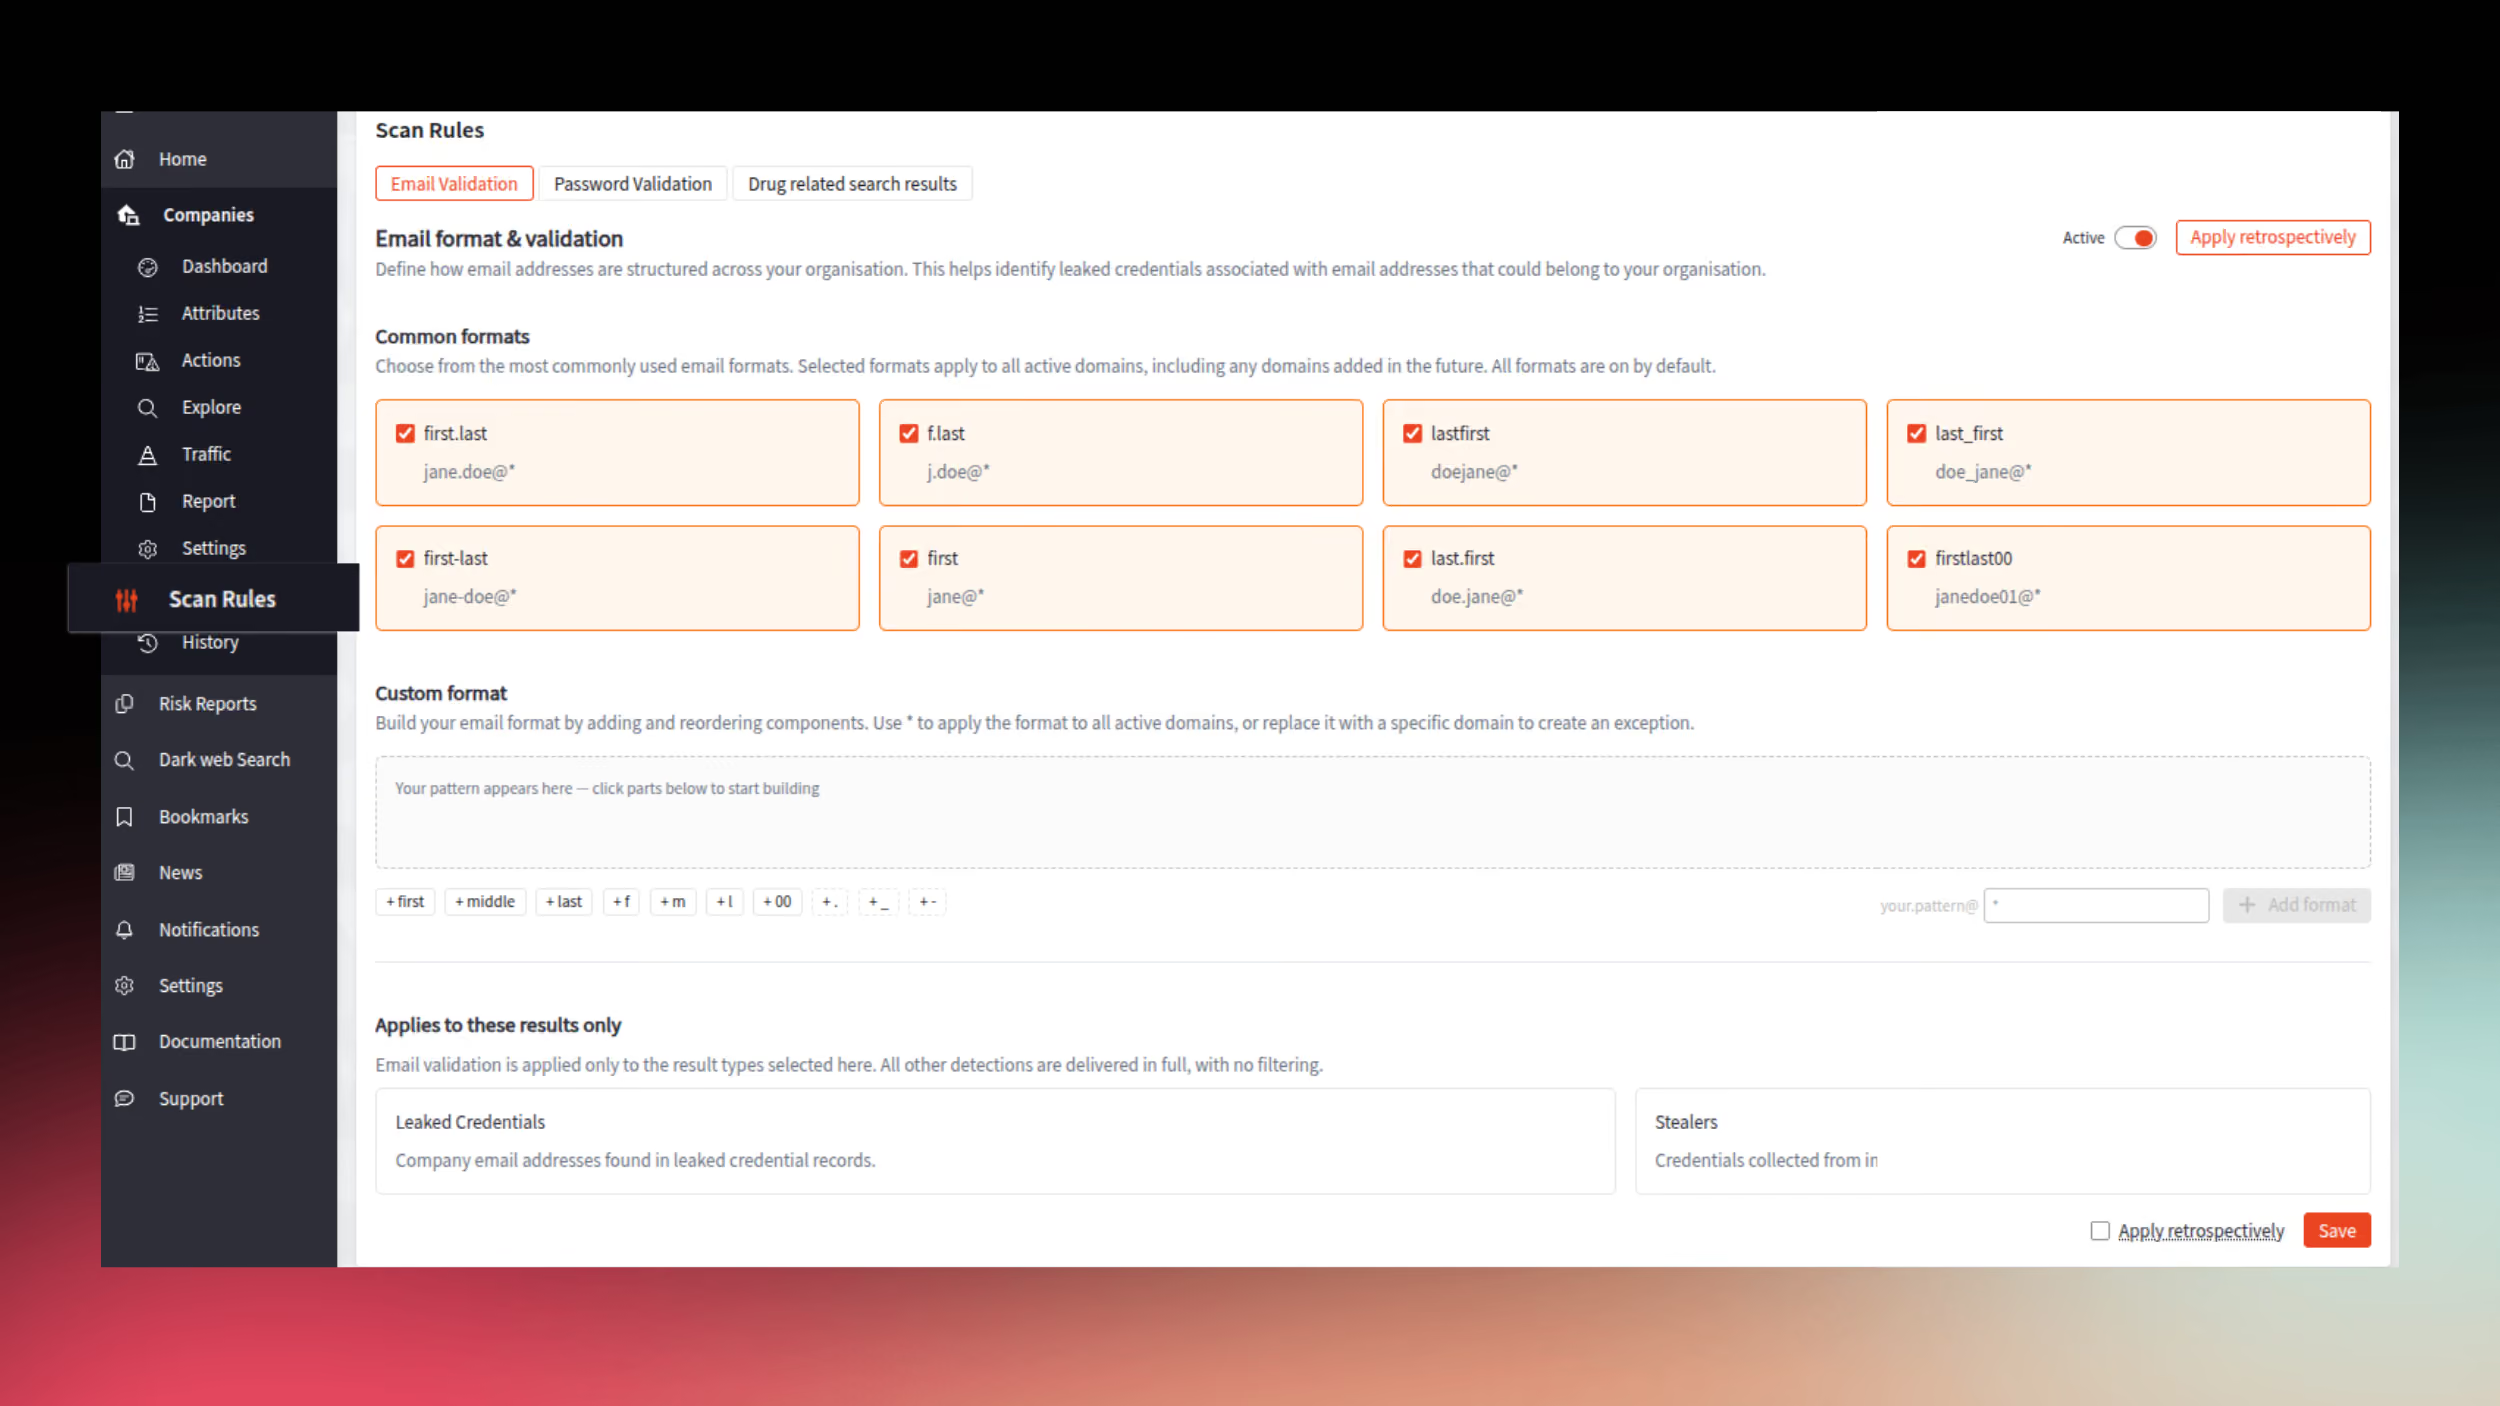
With this enhancement, Searchlight Threat – Monitor customers can drastically reduce the number of false-positive credential results by excluding invalid email formats from their Credential Actions – including the following pre-attack indicators.
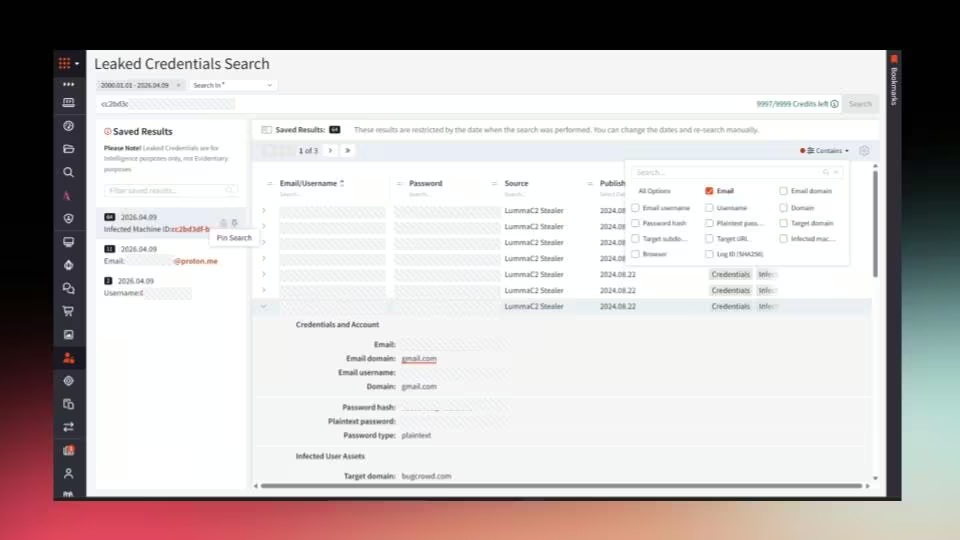
- Leaked credentials: Compromised credentials related to your organization that have been exposed. Stolen username and password combinations remain a significant initial access vector for cyberattacks (HelpNet).
- Stealers: The output of information‑stealing malware that runs on a victim’s device and harvests data, including email addresses, usernames, passwords, and cookies that can be used to launch an attack.
Fewer false positives means less time spent chasing irrelevant results and more confidence that the credentials surfaced in your Credential Actions are worth acting on.
How it works
Users can now define their organization’s email syntax within the new Scan Rules area. For example, if your organization uses the initial.surname[@]company.com format, you can save this format and automatically exclude future discovered results that don’t follow this structure.
For organizations with different email conventions across domains, you can also create customised rules using the custom rule builder. Specific domains can be assigned their own validation rule, while other active domains continue to use the main organization-wide rule. All domains used in these rules must already exist within your active attributes.
These changes are applied at the company level, so MSSPs managing multiple client environments within Searchlight can set different rules for each customer.